Zum jetzigen Zeitpunkt liegen keine Meldungen bezüglich kompromittierter IT-Systeme weder beim Bund noch in der Verwaltung noch bei der regulierten Wirtschaft vor,
sagte ein Sprecher des Ministeriums am Freitag in Berlin.
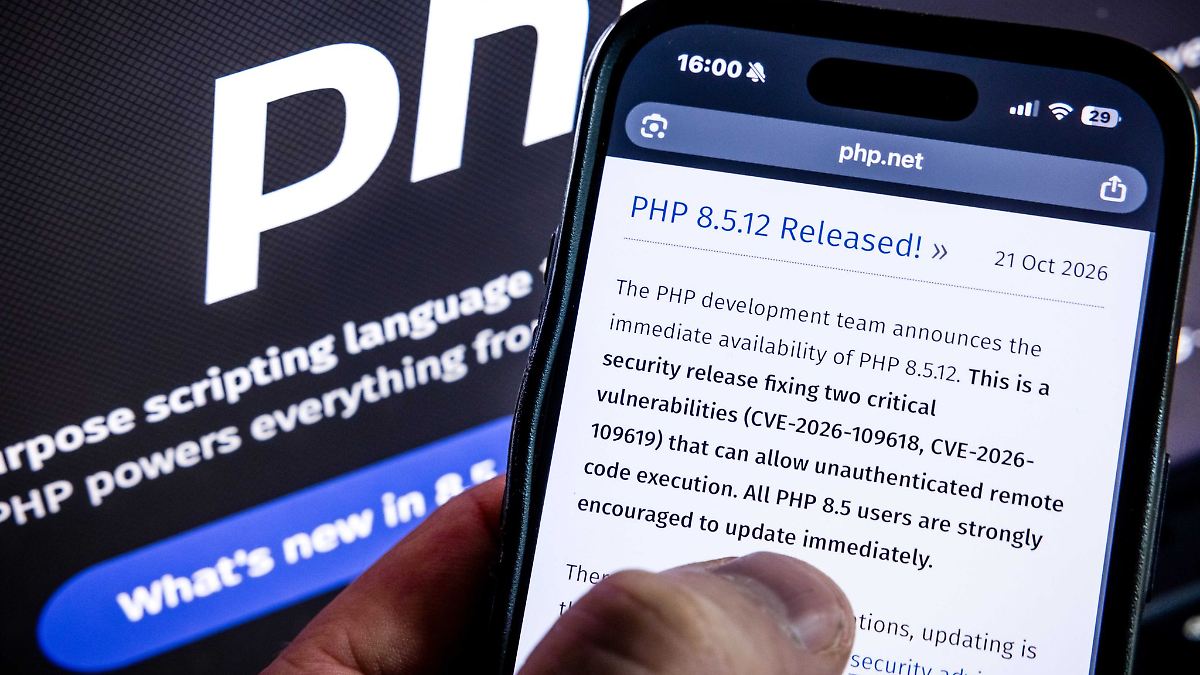
Federal IT systems and regulated industries in Germany have sustained no damage from critical security vulnerabilities discovered in the widely used PHP programming language, according to the German Federal Ministry of the Interior. The announcement follows the discovery of software flaws that endangered websites globally and triggered a wave of defensive measures across public and private sectors.
PHP Vulnerabilities Spark Global Hacker Attacks
Estimates indicate that roughly two-thirds to three-quarters of all websites rely on PHP. Following the disclosure of the software vulnerability, companies, authorities, and organizations worldwide temporarily took their web presences offline to protect their IT infrastructure.

Cybersecurity firm Cloudflare reported that the exposure of the PHP flaws sparked a flood of hacker attacks. Meanwhile, cybersecurity firm Palo Alto Networks estimated that more than 22 million servers and applications worldwide were potentially endangered by the vulnerabilities.
Status of Federal Agencies and Critical Infrastructure
The regulated economy referenced by the ministry includes critical infrastructure such as electricity supply, where operators are required to report hacker attacks immediately. The lack of compromise reports suggests that many operators followed recommendations by installing a software update in a timely manner and recognizing the problem, the ministry spokesperson explained in Berlin.
Authorities and organizations had briefly taken parts of their internet infrastructure offline to safeguard their systems. The spokesperson stated that he could not provide a figure on how many of the internet pages temporarily taken off the net by the federal administration remain offline.
Related reading