Cryptocurrency Hardware Wallet Supply Chain Tampering Leads to $93 Million Theft
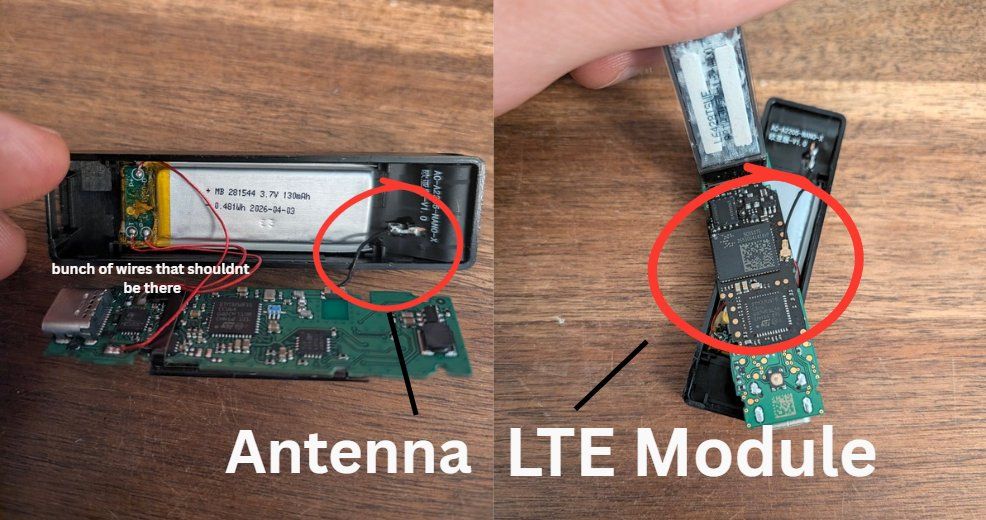
Physical supply chain tampering compromised Ledger hardware wallets, resulting in approximately $93 million in cryptocurrency theft from user wallets, according to a Bloomberg report on October 13. Attackers manually installed unauthorized LTE modules inside brand-new devices distributed through an authorized third-party reseller, allowing the rogue chips to transmit unencrypted recovery seed phrases directly to external command servers.
Unauthorized Cellular Implants Bypass Standard Security Protocols
The security failure surfaced on Friday, October 9, when hundreds of wallets drained simultaneously across the Bitcoin, Ethereum, and Tron networks. Initial investigations revealed that almost all affected devices came from CryptoBilis, an authorized third-party reseller covering Malaysia and Southeast Asia. Ledger ordered CryptoBilis to immediately halt all sales and shipments of the hardware.
UPDATE: I can confirm that the Ledger supply chain is compromised in Europe as well. @Ledger should initiate an immediate product recall to protect users.I just purchased a second device from a different Mediamarkt location today, recorded the unboxing process, and discovered… pic.twitter.com/TjVCx8Hk61
Further investigation led Ledger to announce on October 10 that attackers had inserted a physical hardware implant equipped with a cellular/LTE module. When users generated or verified their 24-word recovery seed phrases during initial setup, the rogue chip recorded the OLED output or read the raw hardware data lines. The integrated cellular chip then transmitted the unencrypted data over LTE networks, granting attackers full remote access to private keys and funds. Because the rogue hardware sat entirely outside the microchip running standard firmware, the modification bypassed Ledger’s automated Genuine Check software protocol.
Ledger Restructures Vendor Verification and Supply Chain Requirements
Following the breach, Ledger confirmed a comprehensive review of its sales policies, chain-of-custody controls, and anti-tampering protections. Ledger CTO Charles Guillemet stated in a social media post that the company is reviewing anti-tampering protection on its devices and advised users with tampered signers to contact support for shipping instructions. In a separate post, Ledger CEO Pascal Gauthier noted that physical supply chain tampering remains a risk for the entire industry, confirming that the company is reviewing direct sales and reseller controls while inviting security researchers and industry vendors to collaborate.
Ledger stressed that its internal infrastructure, firmware code, and direct-to-consumer sales channels through the official Ledger store remain uncompromised. The company instructed distributors to enforce tighter tracking, source units exclusively through approved channels, and strictly ban the restocking or resale of returned units. Meanwhile, users possessing hardware wallets from third-party resellers have been advised to transfer funds immediately to a separate wallet secured by a freshly generated recovery phrase.
Frequently Asked Questions About the Ledger Supply Chain Breach
Which cryptocurrency networks were affected by the simultaneous wallet drains?
The simultaneous wallet drains impacted users across the Bitcoin, Ethereum, and Tron networks on October 9.
How did the rogue LTE chips capture user recovery phrases?
The unauthorized cellular implants recorded the OLED output or read raw hardware data lines as users generated or verified their 24-word recovery seed phrases on the device screen during initial setup.
What action has Ledger taken regarding the third-party reseller involved?
Ledger ordered CryptoBilis, the authorized third-party reseller covering Malaysia and Southeast Asia, to immediately halt all sales and shipments following the discovery of the tampered hardware.
Related reading