European Supermarket Refrigeration Systems Targeted by Cyberattacks
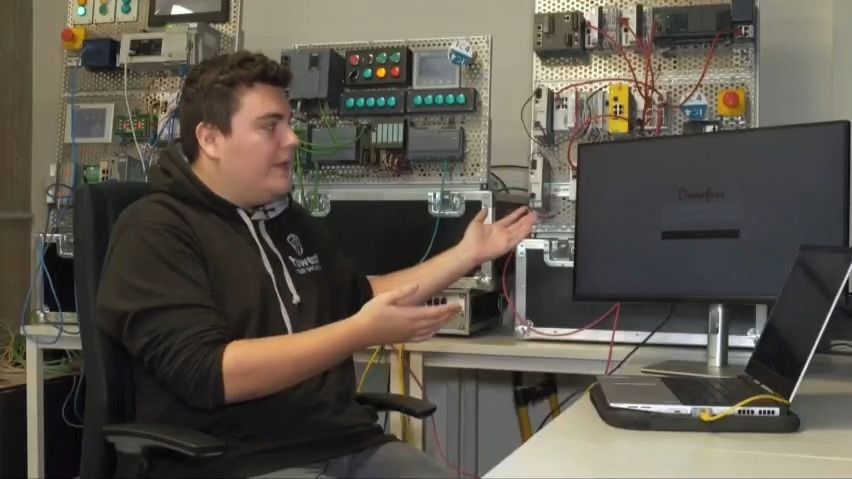
Cyberattacks targeting commercial refrigeration systems have disrupted operations across at least eight European countries, forcing retailers to discard large quantities of spoiled food. The incidents, which began as early as October 11, involve unauthorized access to programmable logic controllers that manage temperature settings in large-scale cooling and freezing units. In a laboratory setting at Howest University in Bruges, researchers showed that by using default credentials—such as the username “admin” and the password “12345”—an attacker can gain full control over a supermarket’s cooling interface within seconds. This access allows for the manual override of temperature controls, enabling attackers to switch units into defrost mode or adjust internal temperatures to extreme levels.
Rising Temperatures and Operational Disruptions
The scale of the disruption has been significant. In Sweden, spokespeople for the retail chains ICA and Coop reported that unauthorized users breached their systems overnight, pushing temperatures in some freezers as high as 55 degrees Celsius, as noted by Financial Times coverage cited via Novinky. Similar breaches were confirmed at Carrefour and Delhaize locations in Belgium, as well as at retail sites in Ireland, the Netherlands, Finland, and Estonia.
The impact has extended beyond grocery stores. Reports from iROZHLAS indicate that three blood plasma storage facilities in France were targeted, with attackers raising temperatures in the cooling units. Unlike the supermarket incidents, the blood banks were able to intervene before the plasma was ruined, thanks to independent monitoring systems that alerted operators to the temperature spikes.
UPDATE: Finland is now also reporting disruptions to supermarket refrigeration systems. Temporary temperature irregularities were detected overnight in some K Group stores. The incidents appear to be on a smaller scale, with the cause still under investigation. Finland now… pic.twitter.com/g23WB0Pk8P
Security Vulnerabilities in Industrial Hardware
The primary vulnerability appears to be the exposure of management interfaces directly to the public internet. Many of these systems, including those manufactured by Danish firm Danfoss, were installed with default factory passwords that operators frequently failed to change. Some units are running legacy software that no longer receives security patches, leaving them susceptible to known exploits.
The European Union Agency for Cybersecurity (ENISA), alongside the European Commission and Europol, has issued a joint statement urging organizations to take immediate action to secure their systems. Authorities are recommending that operators disconnect exposed interfaces from the public internet and implement strong, unique authentication protocols.
The Role of Automated Exploits
Security experts suggest that the recent surge in attacks is facilitated by the increased use of automated tools. Researchers at Howest University noted that artificial intelligence now allows even amateur attackers to generate the code necessary to scan the internet for specific, vulnerable industrial controllers. By searching for publicly accessible web interfaces, attackers can identify targets without needing to know the specific identity of the store owner, often focusing their efforts on specific regions or countries.
While some earlier incidents in 2026 were attributed by experts to the pro-Russian group NoName057, the perpetrators of the most recent November wave remain under investigation.

Old Industrial Controllers Remain Vulnerable Online
Why are these specific cooling systems so vulnerable?
Many industrial refrigeration controllers were designed for long-term use—often 15 years or more—and were never intended to be connected to the public internet. When these devices are placed online without a secure gateway or updated firmware, they remain accessible to anyone who can locate their web-based management portals using standard search techniques.
What should store operators do to protect their equipment?
The primary recommendation from ENISA and manufacturers like Danfoss is to immediately remove the management interfaces from the public internet. Operators are also advised to change all default factory passwords, update to the latest available software versions, and implement network-level security to restrict access to authorized personnel only.
Are these attacks becoming more common?
Security analysts report that while attacks on industrial control systems were previously rare, they are rising in frequency. The accessibility of automated “agentic” AI systems allows attackers to scan for and exploit known vulnerabilities in legacy hardware at a scale that was previously difficult for human hackers to achieve manually.