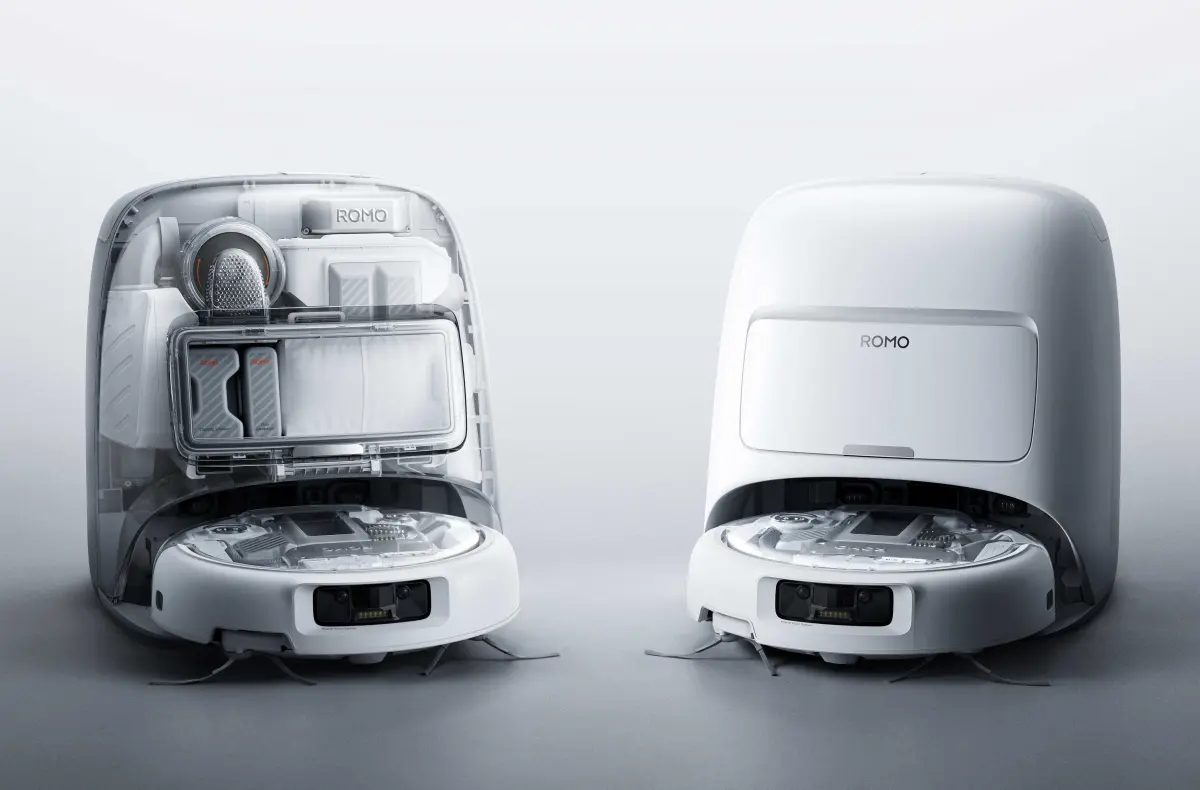
DJI Romo Hack Exposes Security Risks in Robot Vacuums
A security flaw in the DJI Romo robot vacuum cleaner allowed a hobbyist to remotely access and control approximately 7,000 devices worldwide, raising serious concerns about the security of internet-connected home appliances. The incident highlights the growing vulnerability of Internet of Things (IoT) devices and the potential for misuse of sensitive data collected by these devices.
Playful Experiment Reveals Widespread Vulnerability
Sammy Azdoufal, a self-described maker, initially sought to control his newly purchased DJI Romo vacuum cleaner using a PlayStation 5 gamepad. Using Anthropic’s Claude Code AI coding assistant, he reverse-engineered the Romo’s communication protocols. Still, his app unexpectedly connected to DJI’s servers, granting him access to a vast network of Romo vacuums across 24 countries The Verge.
Remote Control and Data Access
Azdoufal discovered he could remotely control the vacuums, view live camera feeds, listen through their microphones, and generate detailed floor plans of the homes they were cleaning. He was able to pinpoint the location of a journalist’s vacuum cleaner and accurately map their home using only the device’s 14-digit serial number Malwarebytes. He reported recording data from 6,700 robots in just nine minutes The Verge.
Technical Failure: Lack of Access Controls
The vulnerability stemmed from a lack of topic-level access controls on DJI’s MQTT message broker. Once authenticated with a single device token, an attacker could access data from all other devices in plaintext Malwarebytes. This meant Azdoufal didn’t need to “break” into the system; he simply leveraged an existing authentication flaw.
Beyond Vacuums: DJI Power Stations Also Affected
The issue wasn’t limited to robot vacuums. DJI’s Power portable battery stations, which utilize the same MQTT infrastructure, were also accessible. These power stations, capable of storing up to 22.5kWh, are designed for home backup power during outages Malwarebytes.
DJI’s Response and Subsequent Patch
Initially, DJI claimed to have patched the vulnerability the week prior to Azdoufal’s public demonstration. However, Azdoufal was able to demonstrate continued access to thousands of devices, including those used by The Verge for testing, shortly after DJI’s initial statement The Verge. DJI later acknowledged a “problem validating permissions on the backend” and implemented a fix the following day.
A Recurring Problem in the IoT Space
This incident is not isolated. Previous security breaches have affected other robot vacuum brands, including Ecovacs, Dreame, Narwal, Samsung, LG, and Roborock. In 2024, hackers took control of Ecovacs vacuums to harass pets and broadcast offensive language Malwarebytes. South Korean authorities also identified vulnerabilities in Dreame, Ecovacs, and Narwal models earlier this year.
The Role of AI in Security Vulnerabilities
Azdoufal utilized AI coding tools, specifically Anthropic’s Claude Code, to reverse engineer the Romo’s protocols. This highlights a growing trend: AI-powered tools are lowering the barrier to entry for identifying and exploiting security vulnerabilities in IoT devices, potentially expanding the pool of individuals capable of probing these systems Malwarebytes.
“It’s so weird to have a microphone on a damn vacuum cleaner,” Azdoufal noted The Verge, raising questions about the necessity of cameras and microphones in these devices.
Keep reading
- Hungary’s First Samsung Onyx LED Cinema Screen Debuts at Lurdy Cinema Budapest
- Bethesda Game Studios Reveals Elder Scrolls VI: Sentinel Subtitle
- FAO Urges Innovation for Food Security and Sustainable Farming (archyworldys.com)
- Shark AV2501S AI Ultra Robot Vacuum Is Discounted by $270 on Amazon (archyde.com)