TeamPCP’s CanisterWorm Targets Iran in Geopolitical Cyberattack
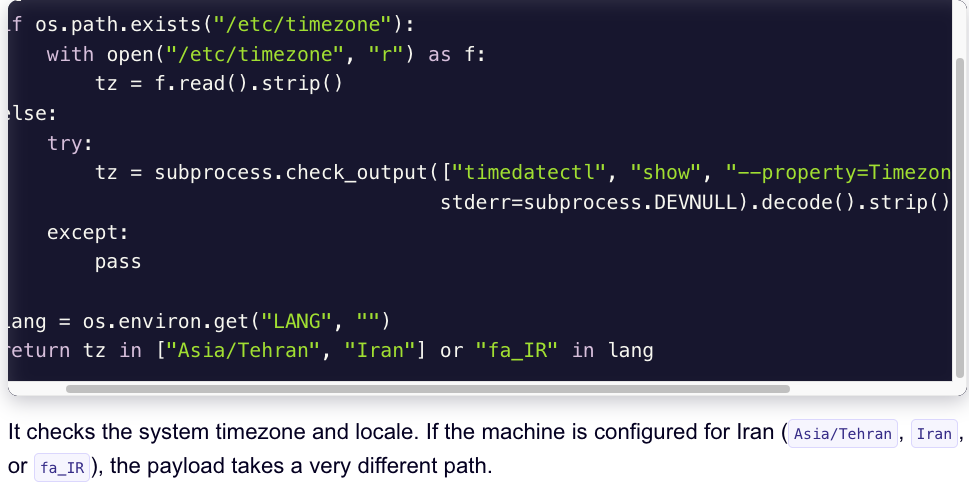
A financially motivated data theft and extortion group is attempting to inject itself into the ongoing geopolitical tensions by unleashing a wiper that spreads through poorly secured cloud services and wipes data on infected systems that use Iran’s time zone or have Farsi set as the default language.
The Emergence of TeamPCP and the CanisterWorm
Experts say the wiper campaign against Iran materialized over the weekend of March 23, 2026 and originated from a relatively latest cybercrime group known as TeamPCP.[1] The group first began compromising corporate cloud environments in December 2025, using a self-propagating worm that targeted exposed Docker APIs, Kubernetes clusters, Redis servers, and the React2Shell vulnerability.[1][2] TeamPCP then attempted to move laterally through victim networks, siphoning authentication credentials and extorting victims over Telegram.
Security researchers at Aikido refer to TeamPCP’s infrastructure as “CanisterWorm” because the group orchestrates their campaigns using an Internet Computer Protocol (ICP) canister — a system of tamperproof, blockchain-based “smart contracts” that combine both code, and data.[3] ICP canisters can serve Web content directly to visitors, and their distributed architecture makes them resistant to takedown attempts. These canisters will remain reachable so long as their operators continue to pay virtual currency fees to maintain them online.
Exploiting Cloud Infrastructure Vulnerabilities
According to security firm Flare, TeamPCP’s strength lies not in novel exploits or original malware, but in the large-scale automation and integration of well-known attack techniques.[1] The group industrializes existing vulnerabilities, misconfigurations, and recycled tooling into a cloud-native exploitation platform that turns exposed infrastructure into a self-propagating criminal ecosystem.[1] Flare’s analysis indicates that 97% of compromised servers are hosted on Azure (61%) and AWS (36%).[1]
Recent Attacks and Supply Chain Compromises
On March 19, 2026, TeamPCP executed a supply chain attack against the vulnerability scanner Trivy from Aqua Security, injecting credential-stealing malware into official releases on GitHub Actions.[1][4] Aqua Security has since removed the harmful files, but Wiz notes that attackers were able to publish malicious versions that stole SSH keys, cloud credentials, Kubernetes tokens, and cryptocurrency wallets from users.[1]
This weekend’s outbreak is the second major supply chain attack involving Trivy in as many months. At the conclude of February, Trivy was hit as part of an automated threat called HackerBot-Claw, which mass exploited misconfigured workflows in GitHub Actions to steal authentication tokens.[4]
Wiz is as well reporting that TeamPCP pushed credential stealing malware to the KICS vulnerability scanner from Checkmarx, and that the scanner’s GitHub Action was compromised between 12:58 and 16:50 UTC on March 23rd.[4]
Geopolitically Targeted Wiping Capabilities
The latest payload deployed by TeamPCP, discovered by security researcher Charlie Eriksen at Aikido, adds a geopolitically targeted destructive component.[3] If the wiper component detects that the victim is in Iran and has access to a Kubernetes cluster, it will destroy data on every node in that cluster.[3] If not, it will wipe the local machine.[3]
Eriksen noted that the malicious canister was rapidly changing, adding new features, and even redirecting visitors to a Rick Roll video on YouTube.[1]
TeamPCP’s Motives and Future Outlook
Eriksen said the people behind TeamPCP are bragging about their exploits in a group on Telegram and claim to have stolen vast amounts of sensitive data from major companies, including a large multinational pharmaceutical firm.[1] The group appears to be motivated by a combination of financial gain and a desire to demonstrate their capabilities.[1]
Security experts observe that supply chain attacks have increased in frequency as threat actors recognize their efficiency.[1] Addressing this trend will require increased vigilance from security firms and a stronger response from platforms like GitHub to identify and mitigate malicious additions to legitimate repositories.[1]
Keep reading